Sign out and end the session
Docs version v1 (main)Nauthera is pre-1.0, in a design-partner programUpdated
An application ends a session through RP-initiated logout at /end_session. With an
id_token_hint that verifies and names the signed-in user, the session ends at once and
no screen shows; with nobody signed in, the browser goes straight on to the
post_logout_redirect_uri. Otherwise (no hint, one that does not verify, or one for
another user) the request lands on /logout to ask the user. See
Sessions, Consent & Logout.
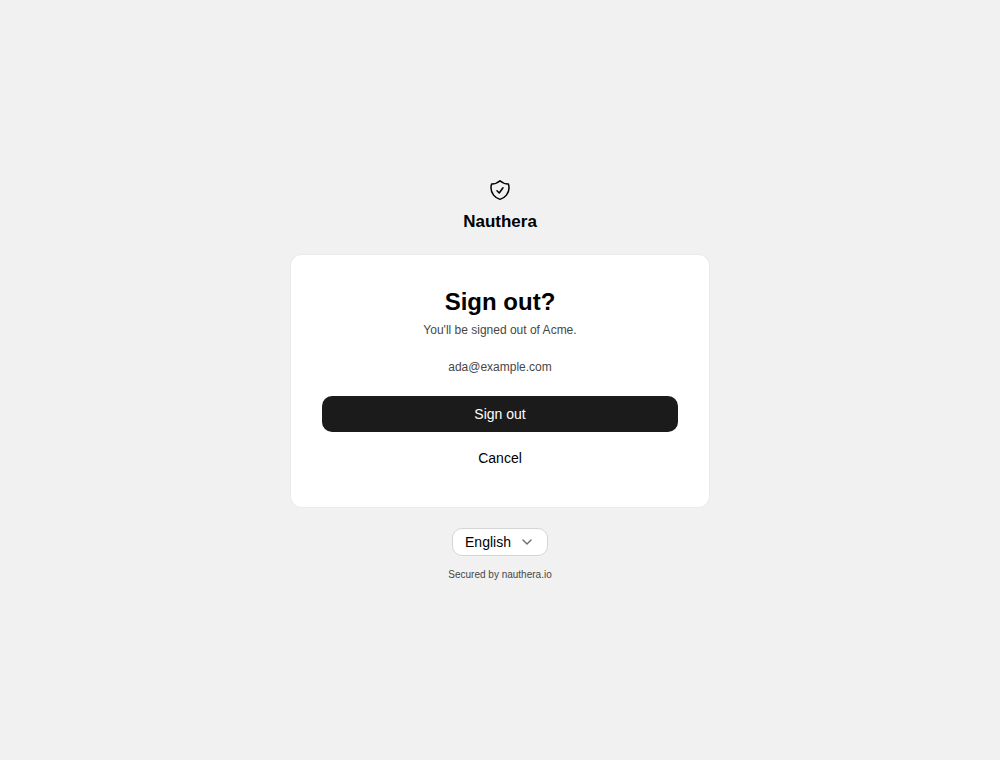
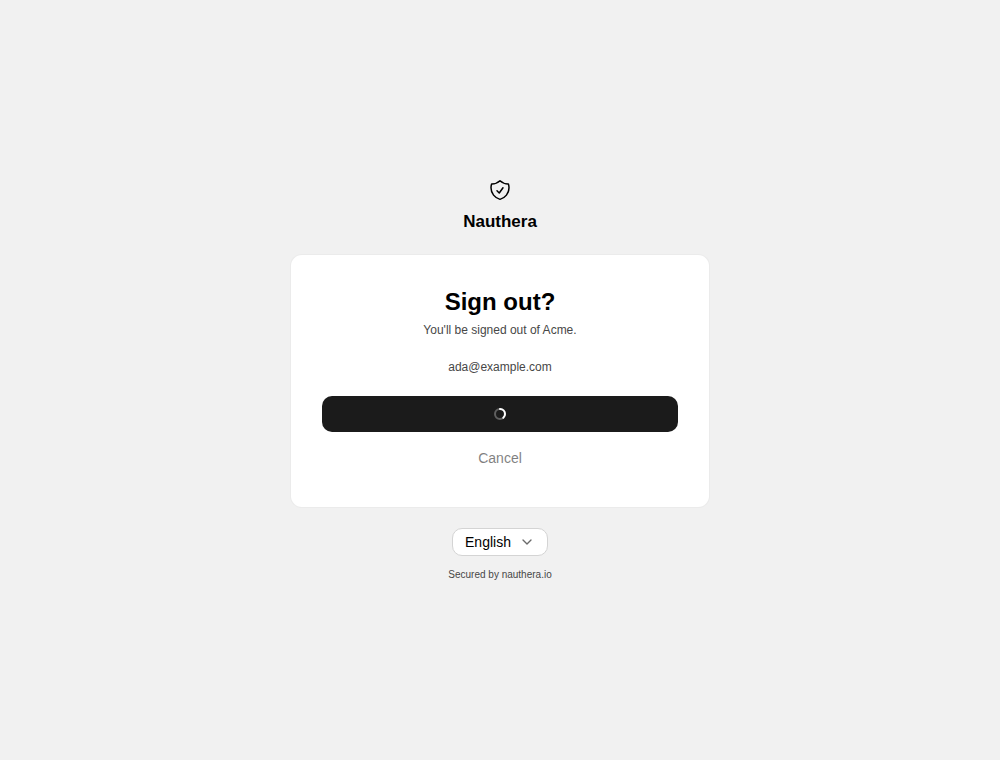
- Sign out ends the session. With a registered
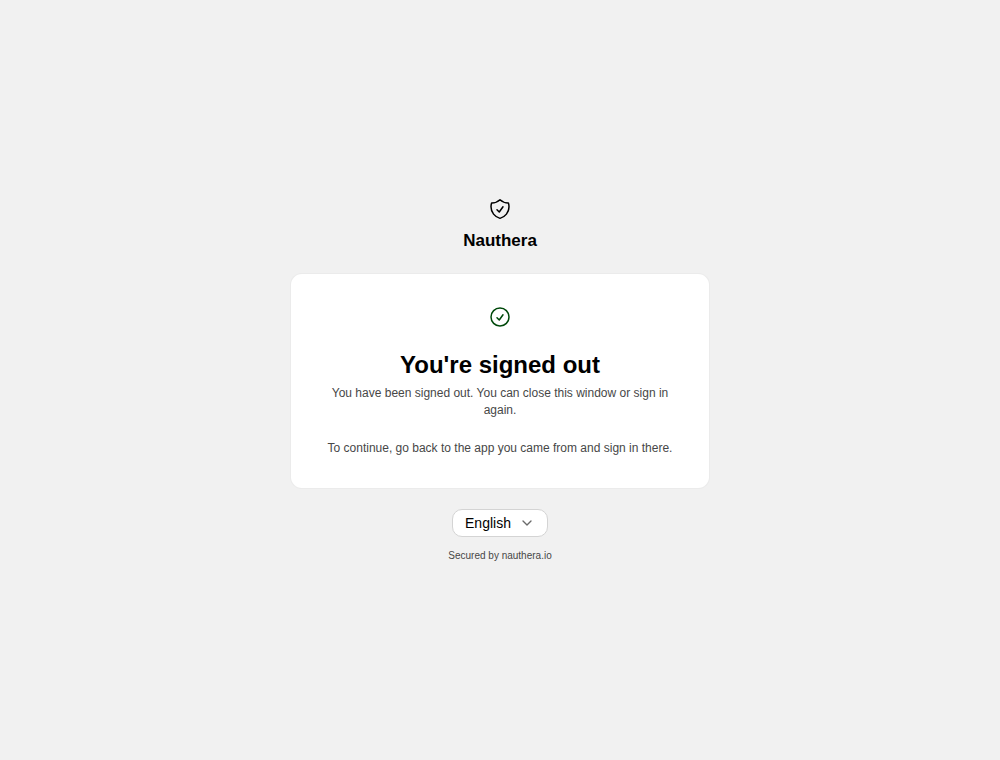
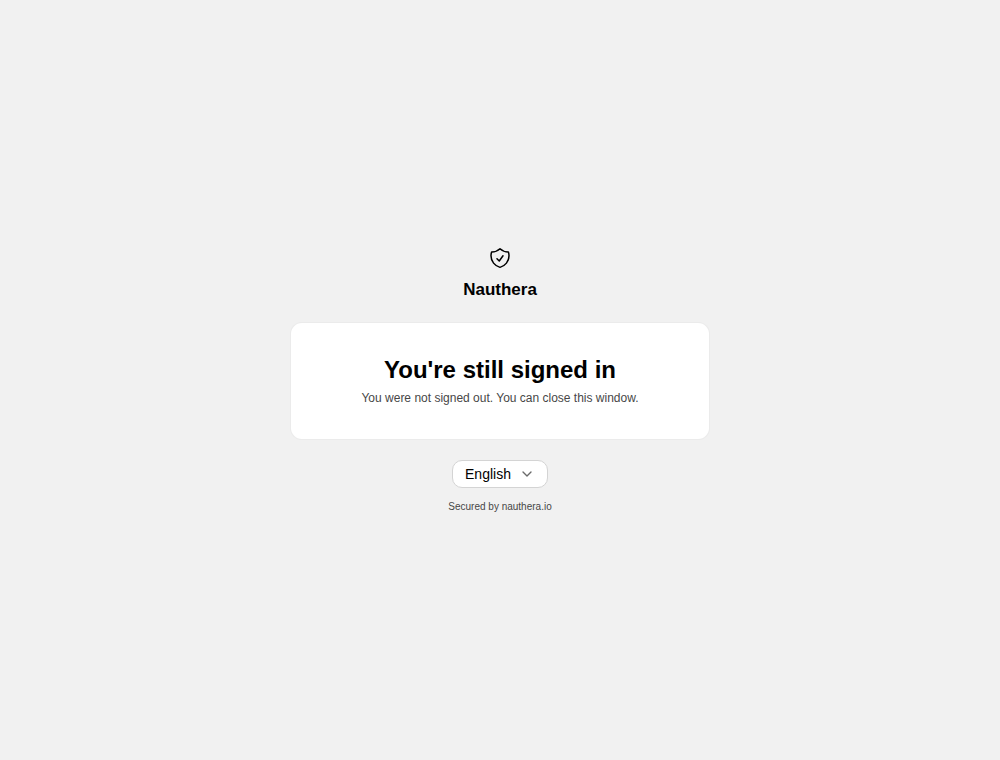
post_logout_redirect_urithe browser goes back to the application; otherwise the page confirms it, with Continue to the application's sign-in or, without one, the way back to the application. - Cancel keeps the session and says so.
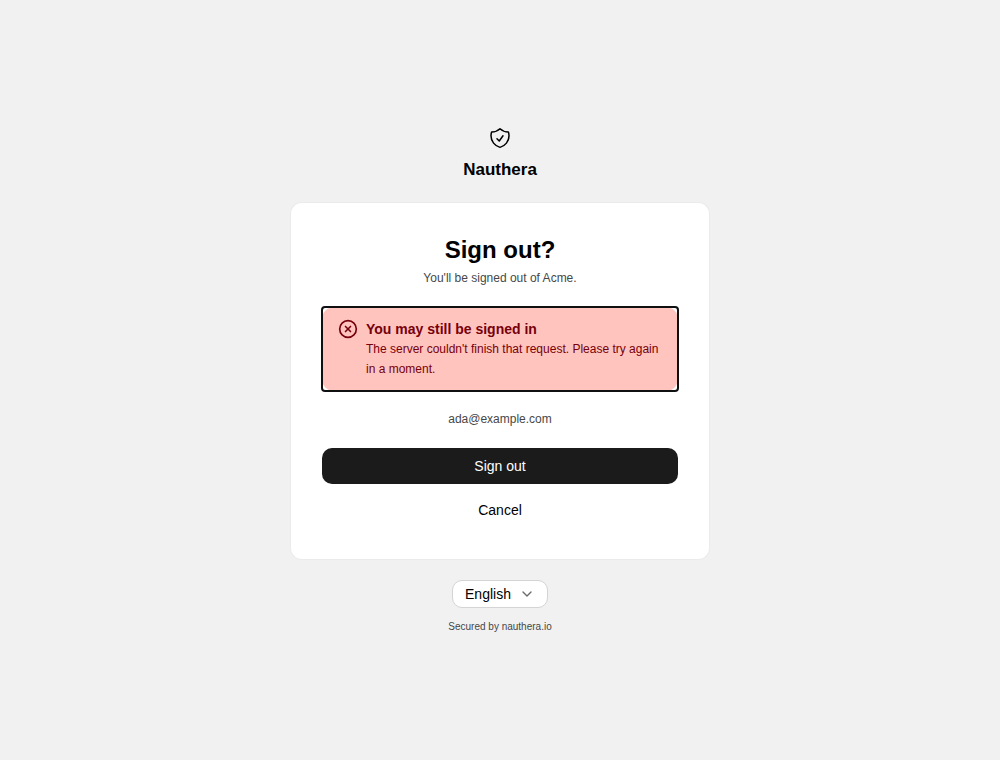
- A sign-out the server could not complete says the user may still be signed in, and offers it again.
Opened without an application's request, /logout is the user's own sign-out: Sign out
ends the session, and Cancel is a link back to sign-in.